▶ project.execute()
> ARVIQ Pentesting Browser (Burp Suite Alternative)_
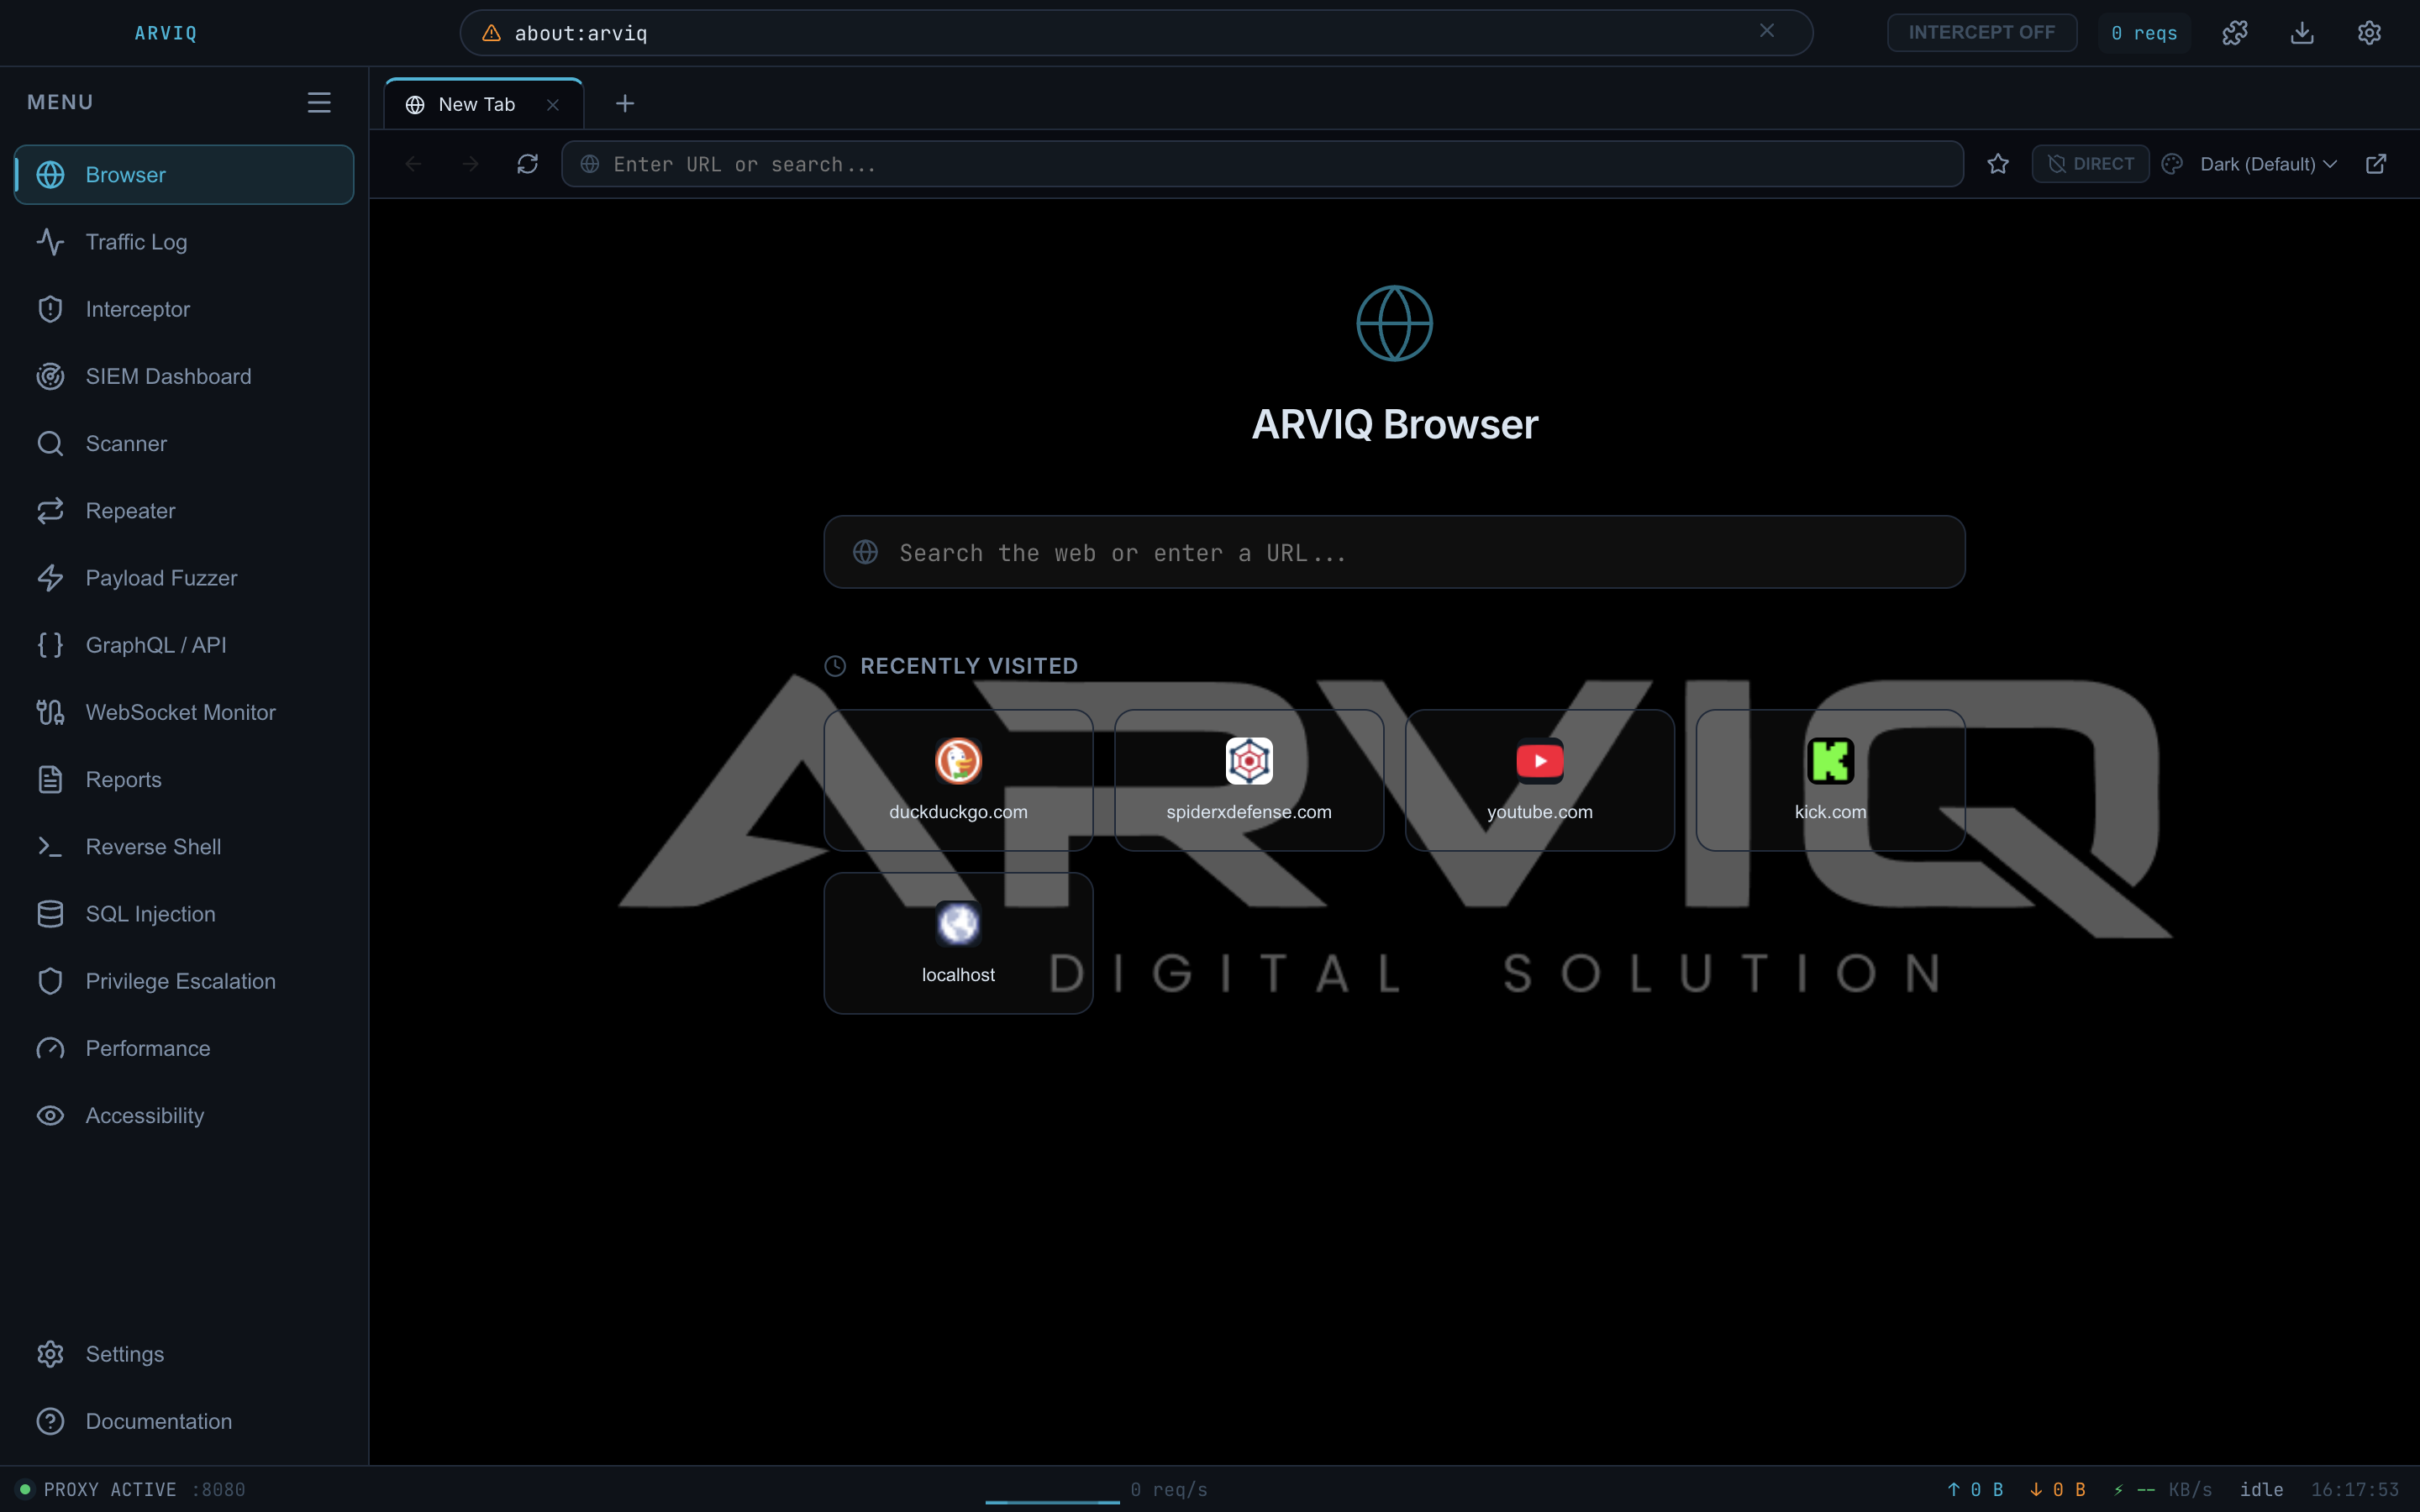
ARVIQ is a security-focused browser with a full professional pentesting toolkit built directly into the browser UI no setup, no configuration needed. It combines the power of Burp Suite's interception capabilities with a modern, accessible interface. Built solo by a B.Tech student in 2+ months, ARVIQ democratizes web security testing with 80+ built-in attack payloads, real-time SIEM threat monitoring, and cross-platform desktop distribution.
//Project_Overview
Problem: Security professionals and students need a $400+/year Burp Suite license just to perform basic web pentesting a massive barrier for learners and indie researchers
Solution: Built ARVIQ, a full security-focused browser with a complete pentesting toolkit built in Payload Fuzzer (80+ XSS/SQLi/SSRF payloads), Live Interceptor, SIEM Dashboard, Vulnerability Scanner, Repeater, WebSocket Monitor, and GraphQL tester
Outcome: Created a free, cross-platform (Windows .exe, macOS .dmg, Linux .AppImage) alternative to Burp Suite built solo as a B.Tech student in 2+ months with all the tools security professionals actually need
//Key_Features
Payload Fuzzer 80+ built-in XSS, SQLi, SSRF, SSTI, and Auth Bypass payloads
Live Interceptor catch and edit HTTP/HTTPS requests mid-flight before they hit the server
SIEM Dashboard real-time threat alerts categorized by Critical, High, Medium, Low severity
Vulnerability Scanner CORS, Security Headers, Cookie Audit, and Reflected Parameter detection
Repeater replay and modify captured HTTP requests with custom parameters
WebSocket Monitor watch, capture, and replay live WebSocket frames
Traffic Log complete chronological request/response history with search and filter
GraphQL Tester introspect and test GraphQL APIs for misconfigurations
Security Reports auto-generate pentest findings reports
Cross-platform: Windows .exe, macOS .dmg, Linux .AppImage
//Challenges_and_Solutions
Challenges
Architecting a custom browser engine (Electron.js) that can intercept, modify, and replay live HTTP/HTTPS requests mid-flight
Building a Payload Fuzzer with 80+ attack payloads covering XSS, SQLi, SSRF, SSTI, and Auth Bypass attack vectors
Implementing a real-time SIEM dashboard that categorizes threats by severity (Critical, High, Medium, Low) from live traffic
Creating a WebSocket Monitor that captures, displays, and replays live WebSocket frames in real-time
Packaging and distributing a cross-platform desktop app as .exe (Windows), .dmg (macOS), and .AppImage (Linux)
Solutions
Used Electron.js as the browser foundation with custom proxy middleware to intercept all HTTP/HTTPS traffic
Built a Payload Fuzzer module with categorized attack payloads: XSS (20+), SQLi (15+), SSRF (10+), SSTI (8+), Auth Bypass (12+)
Implemented SIEM Dashboard with real-time traffic analysis, threat scoring, and severity-based alert categorization
Developed Vulnerability Scanner that auto-checks CORS misconfigurations, missing security headers, weak cookies, and reflected parameters
Created Repeater module to replay and modify captured HTTP requests with custom headers and body manipulation
//Technology_Stack
//Outcomes_and_Impact
Free cross-platform alternative to $400/year Burp Suite democratizing web security testing
80+ built-in attack payloads covering all major OWASP Top 10 vulnerability categories
Real-time SIEM threat detection with severity classification for live traffic monitoring
Zero-setup pentesting open the browser and start testing immediately
Available on Windows (.exe), macOS (.dmg), and Linux (.AppImage) with direct distribution